

Legal and Security
Personal Data Management
Data inventory, privacy notices and consents, data subject requests, a 72-hour breach timer and periodic disposal in one module; viewing sensitive personnel fields is logged with its reason.
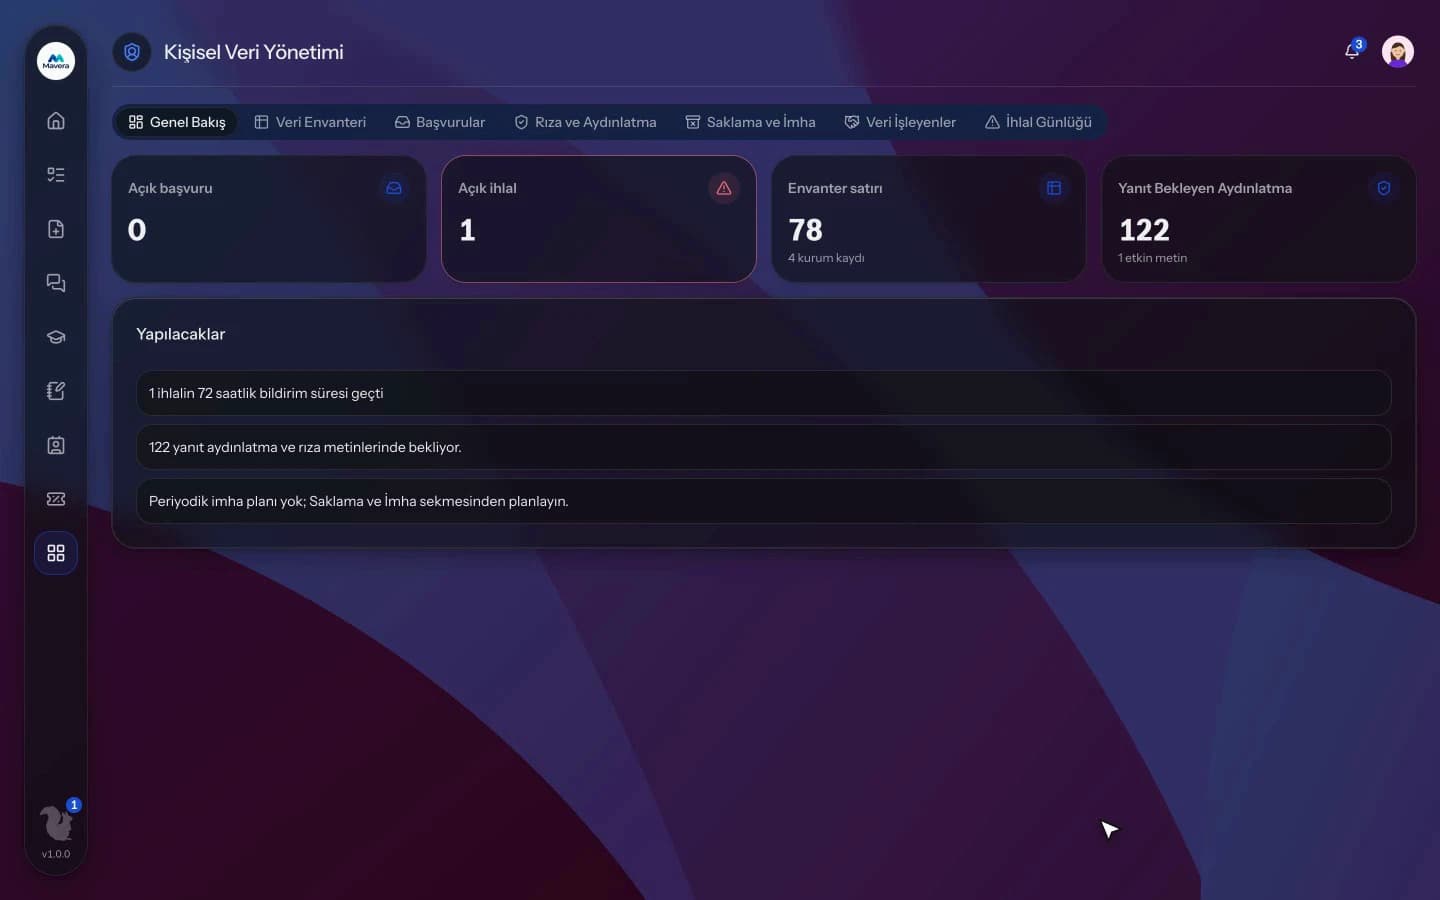
Personal Data Management
How It Works
Complete the inventory
Review the inventory derived from enabled modules and add external processing and processors.
Publish notices
Publish privacy notices and consent texts and collect employee answers.
Manage deadlines
Track request, breach and disposal tasks with timers.
Features
What You Can Do
- The data inventory is derived automatically from enabled modules; add external processing by hand.
- Download the inventory as CSV to support your VERBİS registration.
- Data subject requests are tracked with a 30-day timer and reminders before the deadline.
- Employees submit their own data protection requests from their profile.
- Privacy notices and consent texts are versioned; response counts are tracked.
- Employees withdraw consent from their profile; answers and withdrawals can be downloaded as CSV.
- The retention and disposal policy is generated from the inventory, with periodic disposal tasks every 1–6 months.
- The breach log has a 72-hour notification timer and a PDF notification draft in the authority's form order.
- Record processors with service, shared categories, country and transfer basis.
- Sensitive personnel fields (blood type, disability, health check result) are masked; viewing them requires a reason and each view is written to the Data Access History.
Common Questions
No. Kolekto's Personal Data Management module does not connect to VERBIS directly; your organization, as the data controller, completes the VERBIS registration. The module exports the data inventory, derived from your enabled modules, as a CSV with columns for processing activity, data category, data subject group, purpose, legal basis, recipients, retention period, transfers abroad and measures, which you use as the basis for your VERBIS entries.
When a breach is logged in Kolekto's Personal Data Management module, a 72-hour notification countdown starts from the moment the breach was detected, and the remaining time appears as a to-do on the KVKK overview. A PDF notification draft is prepared with the data controller's details and the breach's start, end and detection times; your organization submits the notification to the Board.
Tenant isolation is enforced in three layers: every query is scoped to the organization and that rule is verified by automated checks before releases; files live in a fully private bucket and are served only through short-lived signed links after an authorization check; file paths are separated per organization too. On top of that: role-based access, hashed session tokens and an audit trail for critical actions. Internal communication messages are stored encrypted on the server; the organization chooses whether conversations are auditable from the admin panel or private.
Access is role-based: only those with HR module permission see employee records, and every employee can access their own. Critical actions are written to the audit log, so who viewed and changed what is traceable.
Your data belongs to you. Each organization's data is kept isolated; on request your data is exported, and at the end of the contract it is deleted in line with regulation.
Start running your company from one place.
In the demo call we agree on your needs and the modules to enable.
Request a DemoContact Us